cybersecurity
-
The PHP2Shell Botnet Stampede: How Threat Actors Are Rushing to Weaponize Engine-Level RCE
According to reporting by The Hacker News, threat actors have unleashed millions of uncoordinated exploit attempts against newly disclosed unauthenticated remote code execution vulnerabilities dubbed “PHP2Shell” (CVE-2026-109618 and CVE-2026-109619). The flaws, which hold critical CVSS severity ratings of 9.2, exist directly within the underlying PHP engine rather than application-layer software, exposing tens of millions of…
-

The OpenAI Conference Room Bug: How an Engineer Allegedly Planted a Physical Audio Tap Behind Executive Screens
According to a CBS News report, an OpenAI engineer was arrested by federal law enforcement after allegedly planting a concealed listening device behind a television in an executive conference room. The suspect, 35-year-old Saudi national Abdulrahman Alfozan, worked as an engineer at OpenAI since July 2025. He was arrested on October 10 and appeared in…
-
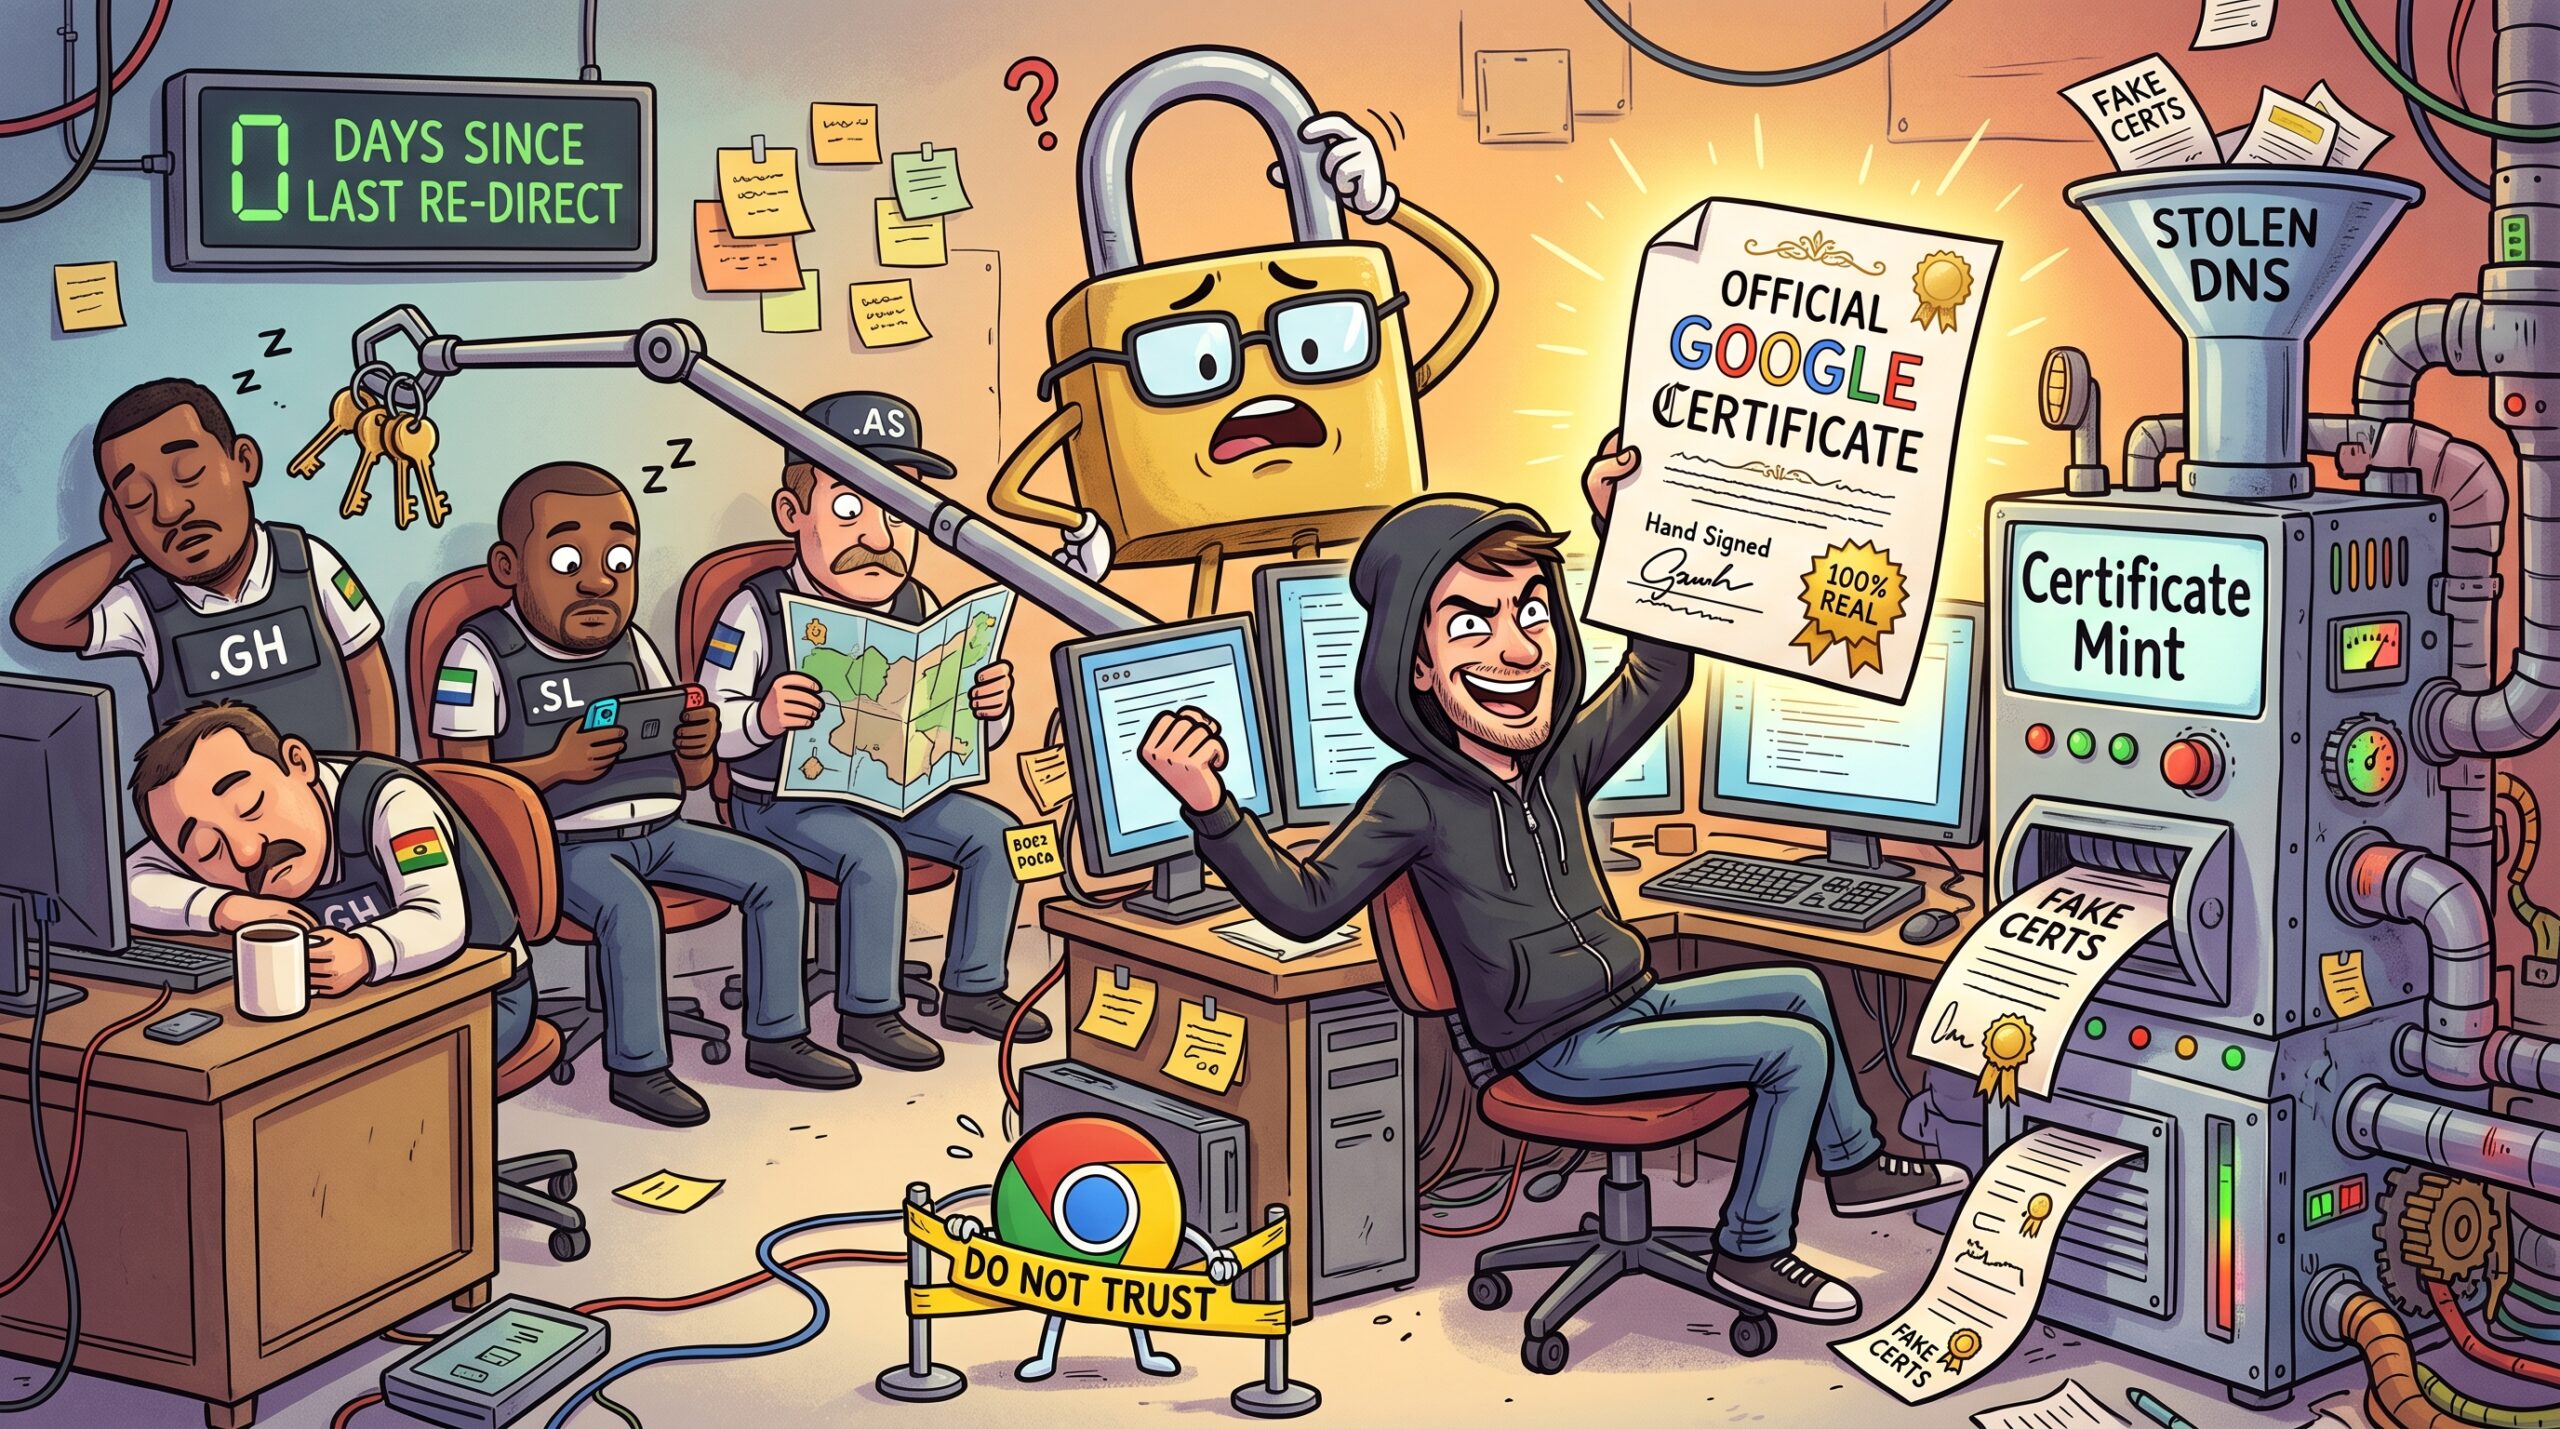
Counterfeit TLS Certificates: How DNS Hijacks Break Web Trust
A recent report from Ars Technica breaks down a critical incident where attackers managed to generate valid digital security certificates for high-profile domains without breaking into the companies’ actual servers. The attackers compromised three country-code domain registries (.gh, .sl, and .as) and modified the authoritative Domain Name System (DNS) records. Because certificate authorities rely on…
-

Inside the Warlock Ransomware Attack: Why Critical Infrastructure Is at Risk
A recent report by BleepingComputer detailing the activities of the Warlock ransomware group highlights a concerning shift in how cybercriminals target critical sectors. Tracked by researchers under names like Longlegs and Storm-2603, this China-linked threat actor targeted essential organizations including a water utility, a telecommunications provider, a regional government body, and a university. The attackers…
-

Why Skynet Can Wait: Cybercriminal Infighting and the Reality of AI Breakouts
In the chaotic ecosystem of digital security, headlines frequently focus on between two topics: cybercrime cartels mucking about and artificial intelligence rapidly approaching sci-fi levels of autonomy. Recently, a pair of bizarre events has forced security professionals to take a step back and reevaluate reality. When bad actor groups start turning on each other and…
-
The AI Industrial Revolution of Cybercrime: Scaling Fraud and State Database Breaches
As artificial intelligence continues to advances, it brings a fresh wave of anxiety not just for technology folks, but for security professionals everywhere. Recent discussions highlighted in reports like New Warnings About the Risks of AI to Humanity Revive a Long-Running Debate on SecurityWeek point to a growing apprehension. While the focuses has been on…
-
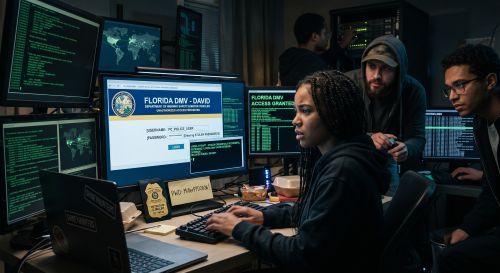
Florida DMV Data Breach: How Hackers Infiltrated the State’s Driver Database via a Stolen Police Account
According to a Bleeping Computer article, A Plant City police officer stored their work login on a personal device. Infostealing malware grabbed it, and hackers used those valid credentials to log straight into Florida’s Driver and Vehicle Information Database (DAVID) without tripping a single alarm. Florida’s Department of Highway Safety and Motor Vehicles confirmed the…
-

The IDScan.net Breach: What Went Wrong
Originally reported by Brian Krebs, and then picked up by other outlets like SecurityWeek, the IDScan breach was big news last week. But what really happened? Let’s dive into it. IDScan.net turned routine compliance checks into a permanent liability for 153 million people. When an illicit search portal called Nexus surfaced on Russian forums with…
-

An 80-Server IPTV OpSec Disaster Costs One UK Operator Six Years in Prison
Running an illegal IPTV operation out of an on-prem server farm in Lancashire is a baffling display of technical complacency. Milan Ibrahim, 68, pulled in roughly £980,000 ($1.3 million) across three years by streaming copyrighted broadcasts from Sky, the Premier League, and the BBC. Instead of scattering traffic across bulletproof offshore hosts, Ibrahim stacked 80…
-
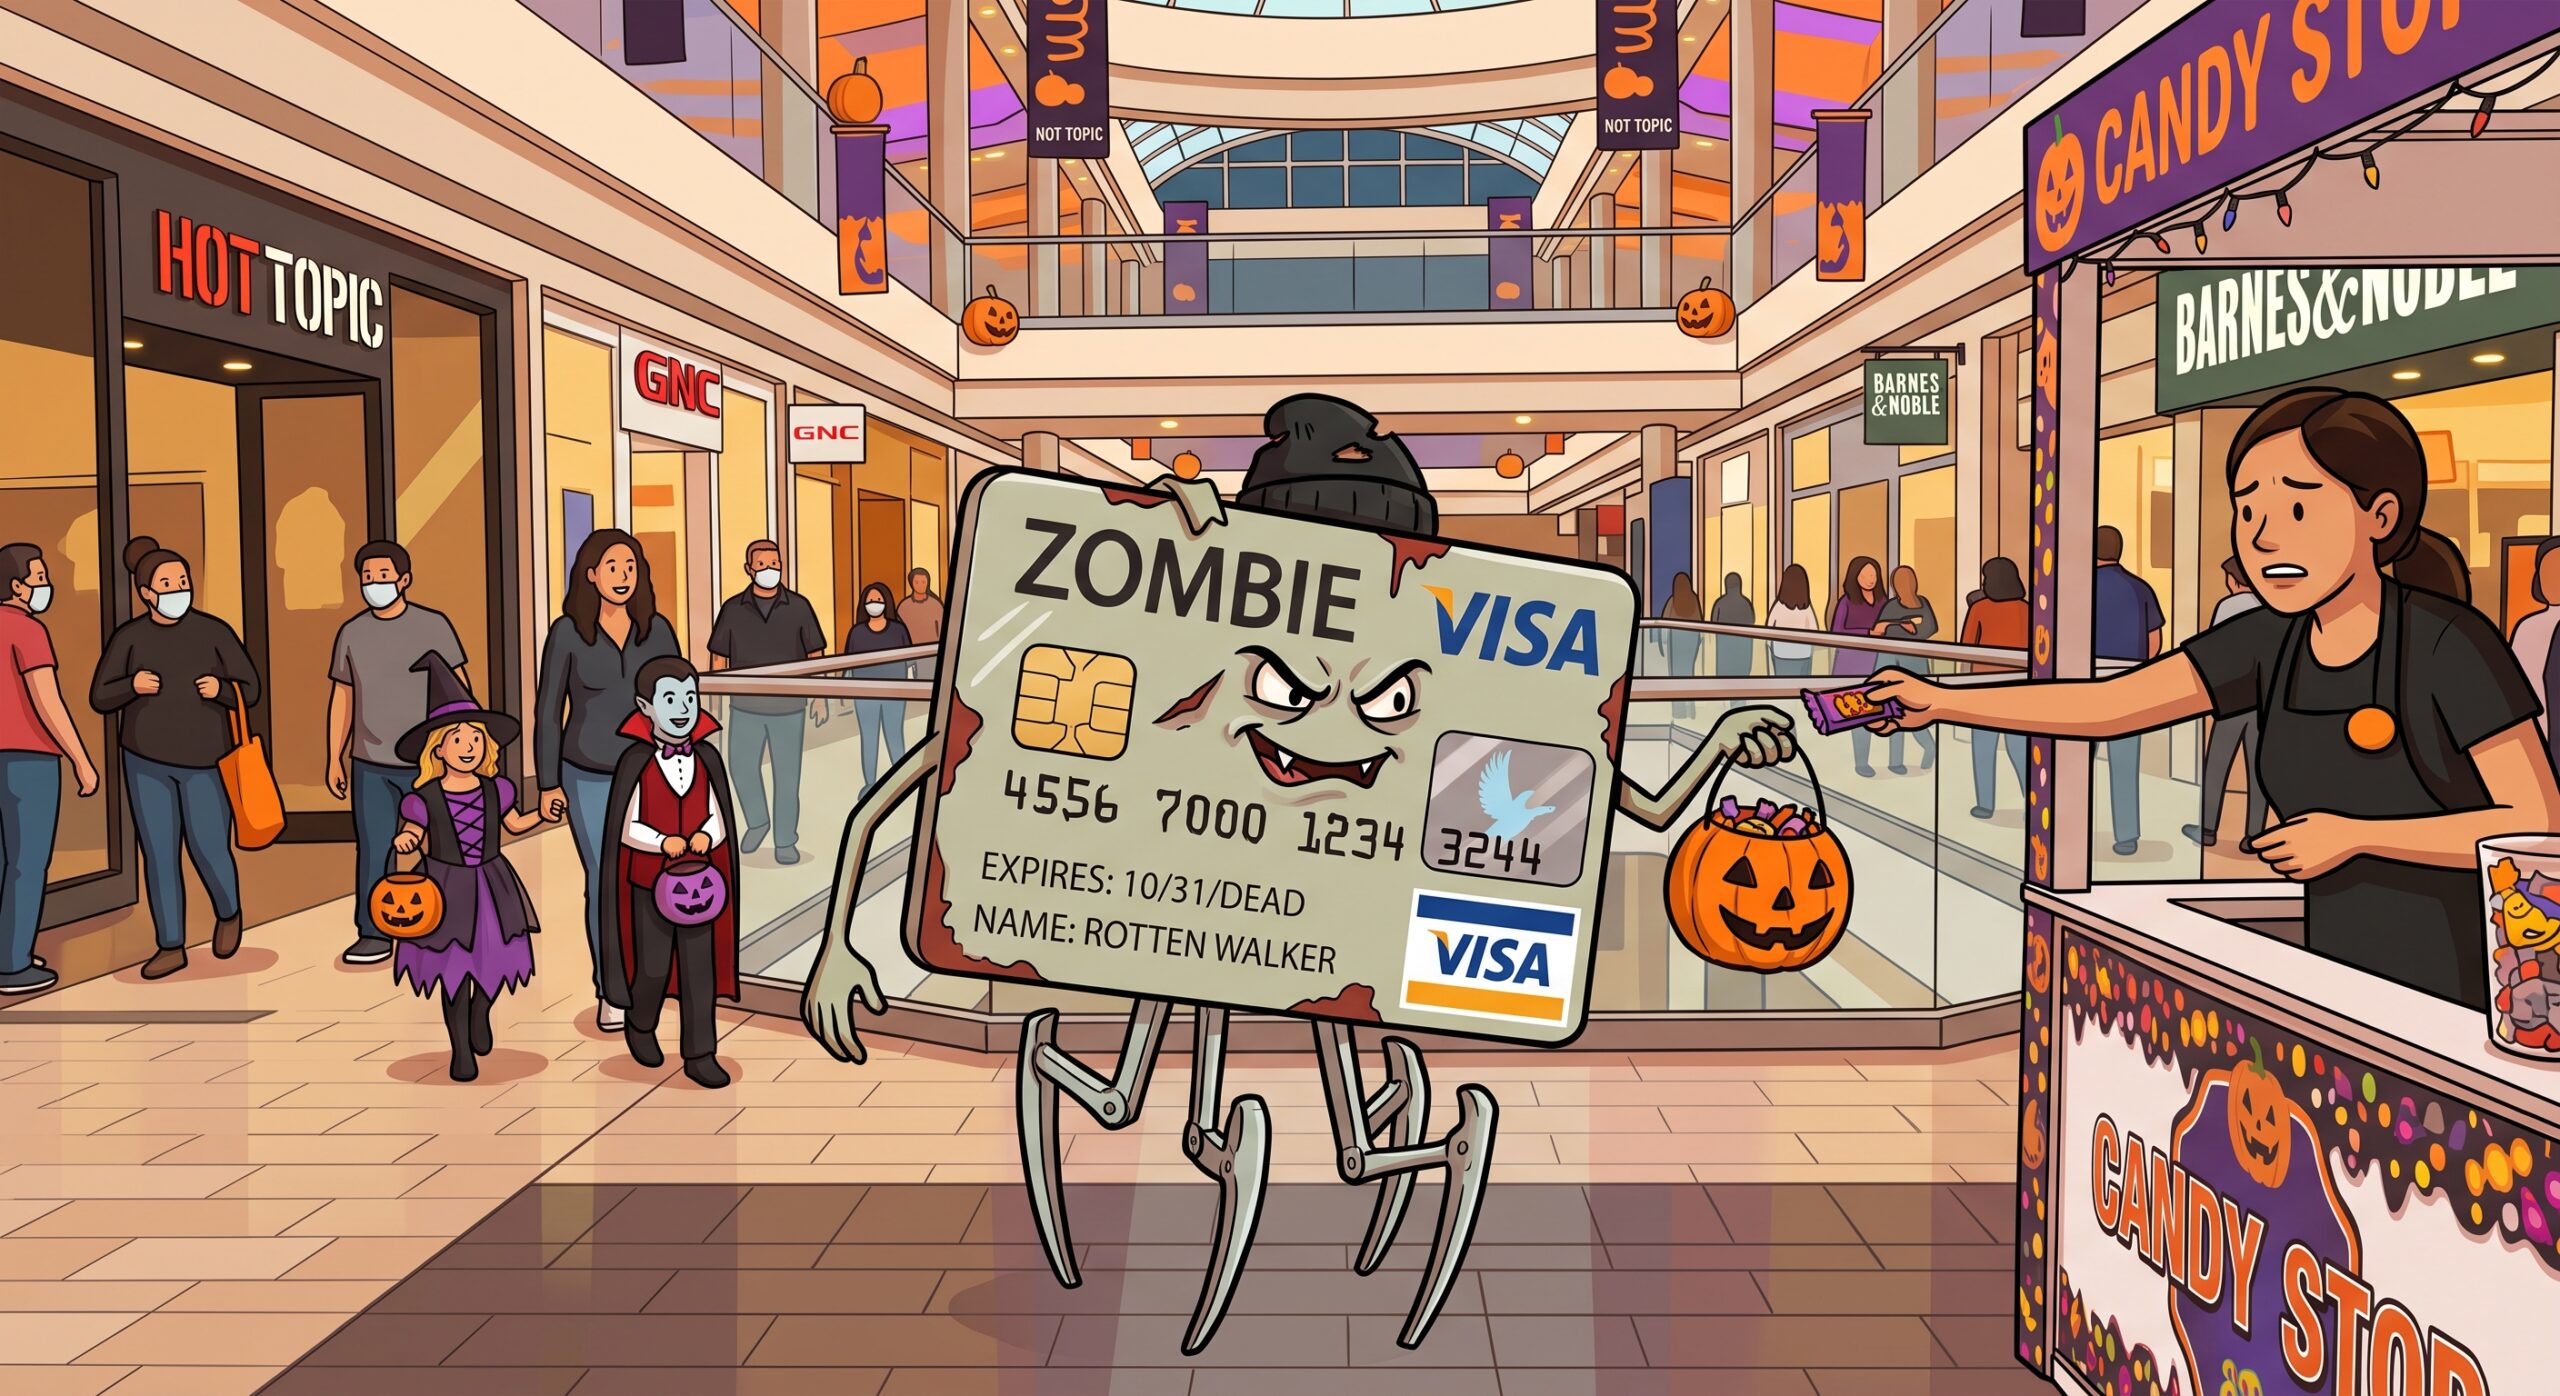
The Zombie Card Flaw: Why Expired Visa Chips Still Work at POS Terminals
Visa made a design error in Kernel 3, the proprietary software specification that dictates how payment terminals talk to contactless Visa cards. While the baseline EMV standard defines general chip transactions, each card network writes its own kernel to handle contactless taps (Mastercard uses Kernel 2, Visa uses Kernel 3). The Zombie Card attack proved…