credential stuffing
-

Chick-fil-A Data Breach Analysis: Credential Stuffing Explained
According to reporting from BleepingComputer (https://www.bleepingcomputer.com/news/security/chick-fil-a-discloses-data-breach-after-credential-stuffing-attacks/), fast-food giant Chick-fil-A recently suffered a security incident caused by automated credential stuffing attacks against its website and mobile app. Credential stuffing occurs when cybercriminals take massive lists of username and password pairs stolen from previous internet leaks and feed them into automated scripts to test if those same…
-
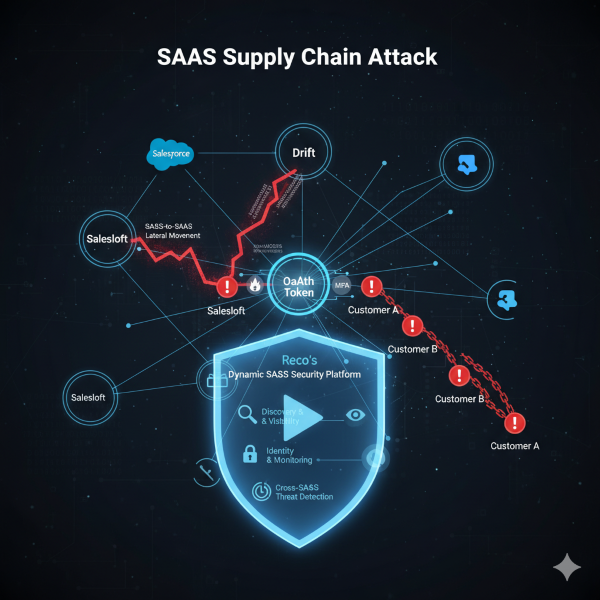
What’s New in Cybersecurity This Week: Projects, Videos, Articles & Podcasts I’m Following – 10/6/25
Welcome to my weekly cybersecurity roundup! Here, I share updates on the projects I’m currently working on, along with the most insightful cybersecurity videos I watched, articles I found valuable, and podcasts I tuned into this week. Featured Analysis Featured article analysis: The Salesloft-Drift Breach: Analyzing the Biggest SaaS Breach of 2025 Analysis of The…
-

What’s New in Cybersecurity This Week: Projects, Videos, Articles & Podcasts I’m Following – 6/2/25
Welcome to my weekly cybersecurity roundup! Here, I share updates on the projects I’m currently working on, along with the most insightful cybersecurity videos I watched, articles I found valuable, and podcasts I tuned into this week. Featured Analysis Featured article analysis: Largest ever data leak exposes over 4 billion user records The recent exposure…
-
What’s New in Cybersecurity This Week: Projects, Videos, Articles & Podcasts I’m Following – 3/24/25
Welcome to my weekly cybersecurity roundup! Here, I share updates on the projects I’m currently working on, along with the most insightful cybersecurity videos I watched, articles I found valuable, and podcasts I tuned into this week. Featured Analysis Featured article analysis: Mike Waltz takes ‘full responsibility’ for Signal group chat leak The accidental inclusion…
-
Smishing Example
What is Smishing? Smishing, a portmanteau of “phishing” and “SMS,” the latter being the protocol used by most phone text messaging services, is a cyberattack that uses misleading text messages to deceive victims. The goal is to trick you into believing that a message has arrived from a trusted person or organization, and then convincing…